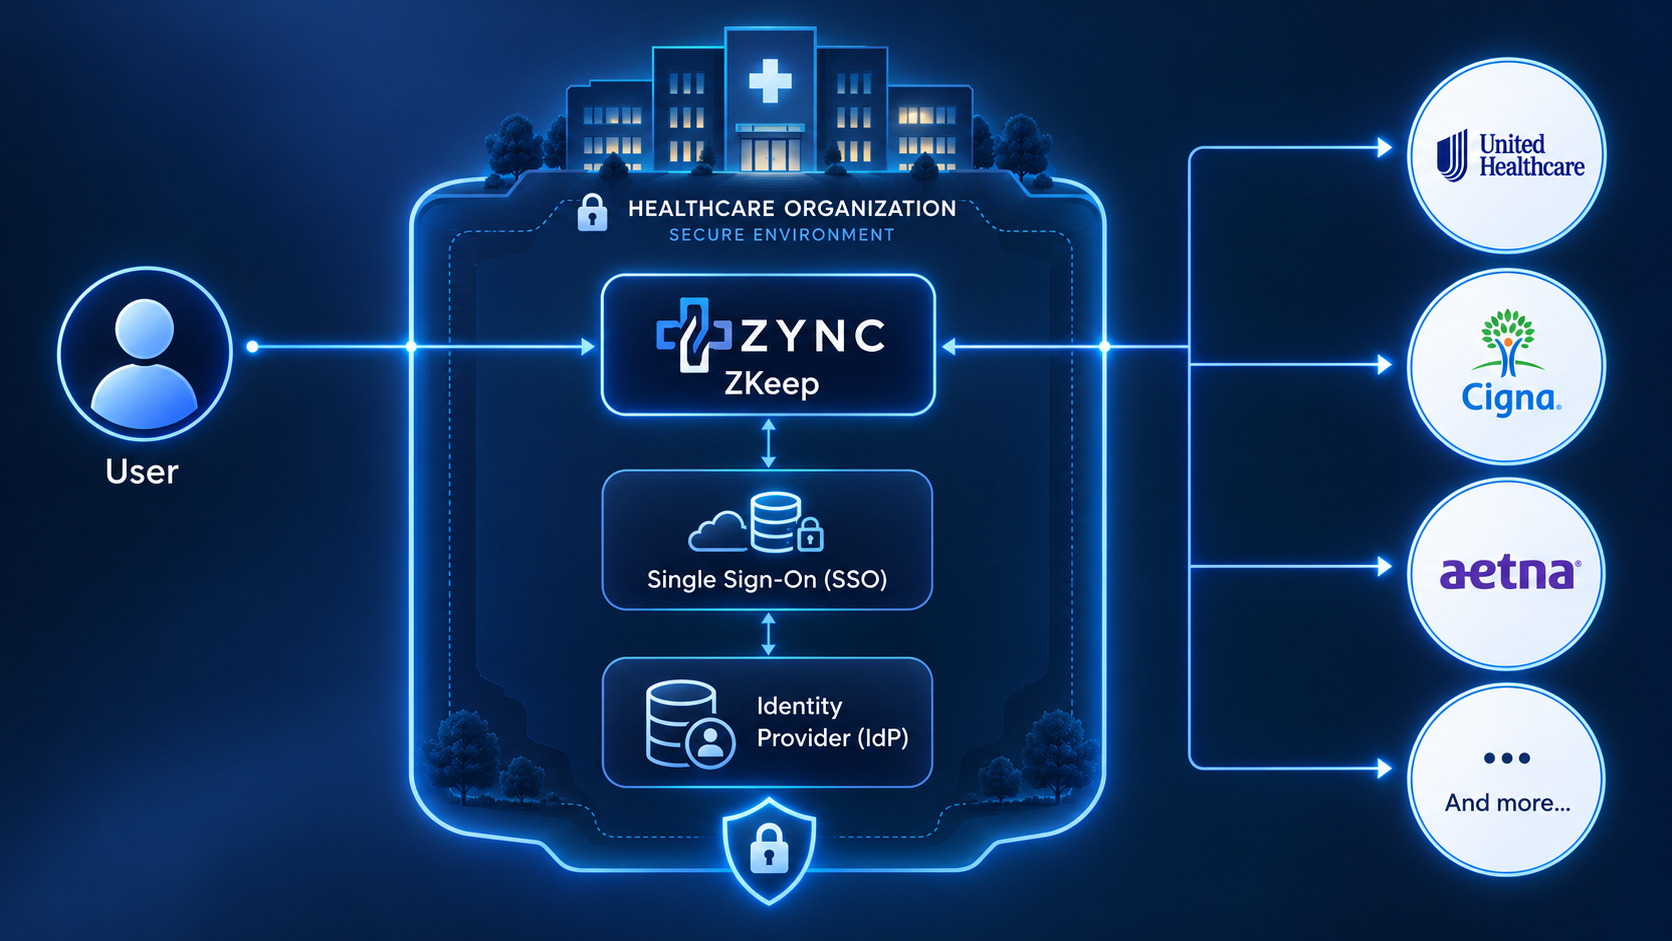
ZKeep integrates with your organization’s existing identity provider to give users secure, streamlined access to ZKeep using the same corporate authentication process they already know.
With SAML 2.0-based SSO, organizations can centralize authentication, strengthen access controls and reduce password-related risk while giving users a simpler path to the payor portals and external applications they rely on every day.
ZKeep works within your existing identity strategy rather than creating another standalone login environment.
Users authenticate through your organization’s identity provider, and ZKeep uses that trusted authentication to provide access to the external portals and websites assigned to them.
This helps extend centralized identity governance beyond your internal applications and into the external websites your workforce accesses every day.
The flow
How SSO works with ZKeep.
01
User authenticates
The user signs in using your organization’s corporate identity provider.
02
Identity is verified
Your IdP validates the user and issues a secure authentication token.
03
ZKeep grants access
ZKeep recognizes the authenticated user and provides access to the portals and external sites assigned to that individual.
04
The user gets to work
From ZKeep, users launch approved payor portals and other external sites without managing another set of ZKeep credentials.
This process is supported through SAML 2.0 authentication.
The payoff
One identity. Controlled access.
Stronger security
Authentication remains centralized through your trusted identity provider.
That helps reduce the need for additional passwords and gives IT greater control over who can access ZKeep.
Simpler user experience
Users authenticate through the same corporate identity environment they already use and gain access to their assigned ZKeep resources.
Less login friction. Fewer passwords to remember.
Easier access management
Centralized authentication simplifies user access administration and supports stronger enterprise security policies.
Faster offboarding
When a user's corporate identity access is terminated, their access to ZKeep can also be removed as part of the same identity lifecycle.
Compatibility
Works with your existing identity provider.
ZKeep supports SAML 2.0-compliant identity providers, allowing healthcare organizations to integrate ZKeep into their existing authentication environment. Common examples include:
Microsoft Entra ID
Okta
Amazon Cognito
Cisco Duo
Citrix
SecureAuth / Arculix
Other SAML 2.0 platforms
The gap it closes
Extend identity governance beyond your network.
Traditional SSO is highly effective for internal enterprise applications. The challenge is that healthcare teams also depend on dozens of external payor portals and third-party websites that sit outside the organization’s network. ZKeep helps bridge that gap.
Your organization continues to control who the user is through your identity provider. ZKeep then controls which external portals and sites that user can access.
Identity Provider
Authenticates the user.
ZKeep
Controls and executes access.
External Portals
Remain outside the organization, but access is governed through ZKeep.
That distinction is one of the most important security benefits of the ZKeep model.
What comes with it
Better security without more friction.
ZKeep combines SSO with capabilities designed specifically for external healthcare access:
SAML 2.0 authentication
Role-based access
Credential concealment
Centralized portal administration
MFA support
User provisioning
One-click access revocation
Audit and usage reporting
Third-party access controls
Integrated authenticator capabilities through ZKeep Verify
The result is a more controlled external-access environment without making portal access more difficult for users.
Enterprise healthcare
Fit into the identity infrastructure you already have.
Healthcare organizations already invest heavily in identity and access management. ZKeep helps extend that investment to the external websites that revenue cycle, administrative, clinical support and third-party teams rely on every day.
Rather than creating another disconnected authentication process, ZKeep fits into the identity infrastructure you already have.
IT and security FAQ
If something here is not covered, the sales team can walk the specifics against your own automation stack.